

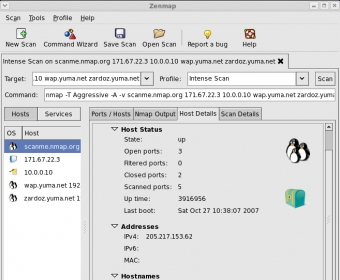
Manage your network by scanning and identifying hosts and services. Send packets, analyze the responses, detect firewall types and pocket filers, as well as the uptime of the system and the operating system. Use the Nmap Script Engine tool to create your own scripts and customize your scanning processes and save your analysis results.
Gordon Lyon (known in the Internet by his other name, “Fyodor”) is the man who maintains the leading Nmap Security scan tool. The project started in 1997 as a mere port scanner for Linux and bearing no version number. Due to its popularity and high demand, they started developing the product. The growing rate of users made Nmap to devise a GUI version called "Zenmap", which was originally derived from Umit, a developed between the 2005 and 2006 Nmap Summer of Code, sponsored by Google.
Nmap can perform network inventory, list a service history, identify firewall types and pocket filers, and detect the uptime of the system and the OS. Its huge database may identify the OS fingerprints of the target system easily and reliably.
You can save your Nmap analysis output for later use, or just keep it as a reference. With its port scanning functionality, Nmap can find out which ports are open (both TCP and UDP) in the target systems. Depending on the switch used, you can really do “a brute force method” to actually identify the weaknesses of a system. Once you have done that you can close the unnecessary ports, so that you or your organization do or does not become any hacker’s next victim. more




Comments (1)